Blog & News
Recent developments, analysis, and updates from the world of cybersecurity and AI safety.

A newly disclosed flaw, nicknamed "sshole," affects OpenSSH on musl-based Linux systems such as Alpine. Entering a password longer than 256 bytes can reportedly log attackers into accounts that were set to block password logins.

Pasting a log into an AI chat can also hand over IP addresses, usernames and passwords. Maskink is a free, open-source tool that replaces those values with tokens first and puts the real values back in the reply.

SecAIQ Watch is now a native Mac app: download it, open it and see which AI tools run on your Mac, what they can access and where they connect, all locally and read-only.

Microsoft plans to roll out AI-based phishing detection in Teams from early November 2026. It looks at conversation context to catch social engineering and impersonation, even when no malicious link or file is present.
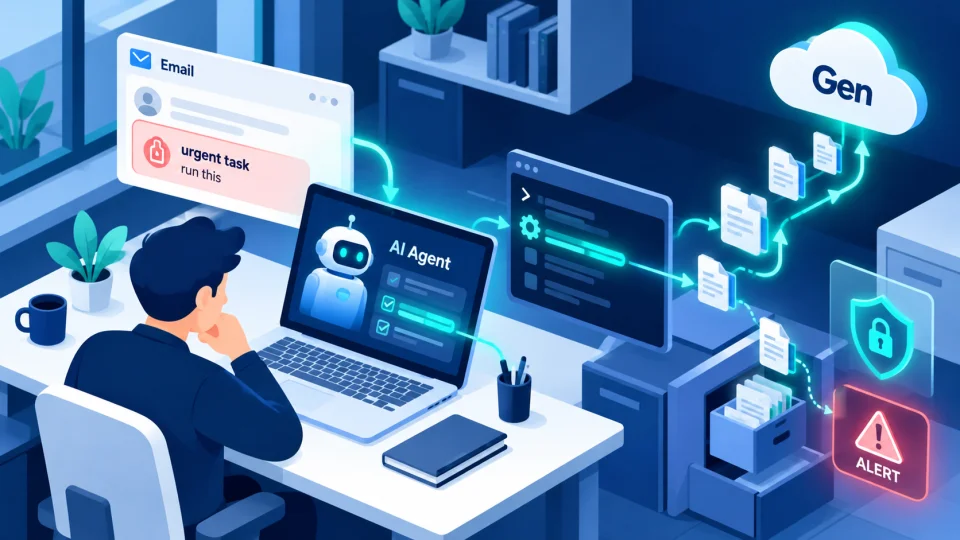
Researchers at Gen Threat Labs showed an AI agent can be tricked by email content into running commands and deleting files. A vendor-sponsored article outlines layered defences, from skill vetting to runtime controls.

SecAIQ is now a free mobile app for iPhone, iPad, Android phones and Android tablets: plain-language security and AI safety guides, free tools, a glossary and news, with no account needed.

Organisations are being urged to act now on a critical PHP issue that could allow attackers to execute commands on web servers. All PHP versions are affected and a fix has been released.

ISO/IEC 27090:2026 gives guidance on cybersecurity threats specific to AI systems. For organizations already running ISO/IEC 27001 and 42001, the most efficient path is to extend what they have rather than build new standalone structures.
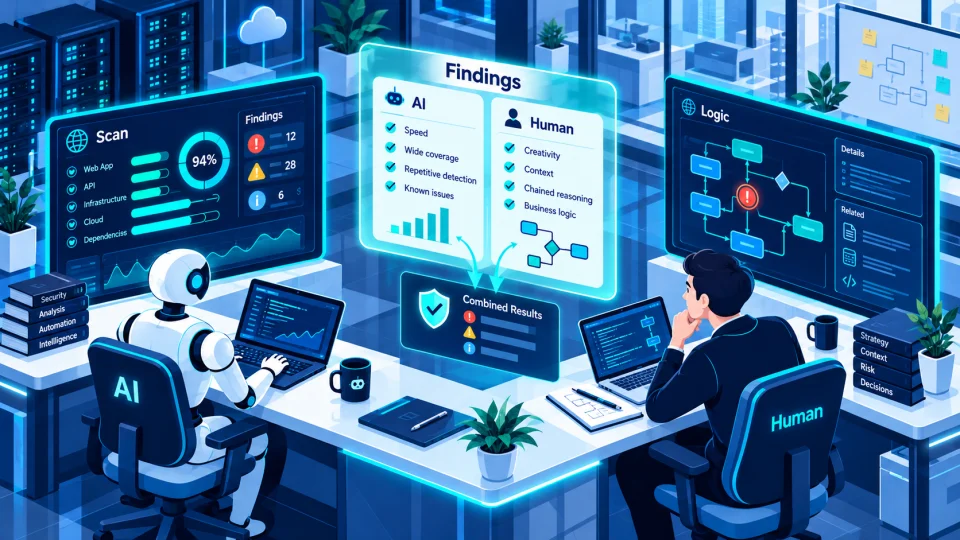
A new comparison of AI-driven and human penetration testing finds each approach has distinct strengths, suggesting the two work best together rather than as substitutes.