Blog & News
Recent developments, analysis, and updates from the world of cybersecurity and AI safety.

Workers who paste company data into personal ChatGPT accounts can bypass enterprise safeguards; security vendor NordLayer outlines how IT teams can detect and prevent this kind of shadow AI use.

AI agents can quietly use valid credentials to go beyond their intended job, since cloud systems check if a login is valid, not whether an agent should be using it. Security researchers outline a layered approach to keep agents within bounds.

A phishing campaign uses fake AI assistant websites and browser-in-browser tricks to steal advertising account logins and MFA codes from agency staff and media buyers.

Employees routinely connect SaaS apps and AI tools via OAuth, creating thousands of hard-to-track access grants per company. Security researchers warn this backlog is a growing breach risk and outline how automation can help teams keep up.

Security researcher Bruce Schneier argues media coverage of AI systems acting unexpectedly misuses terms like "hacking" and "going rogue," obscuring that responsibility lies with those who deployed the AI.
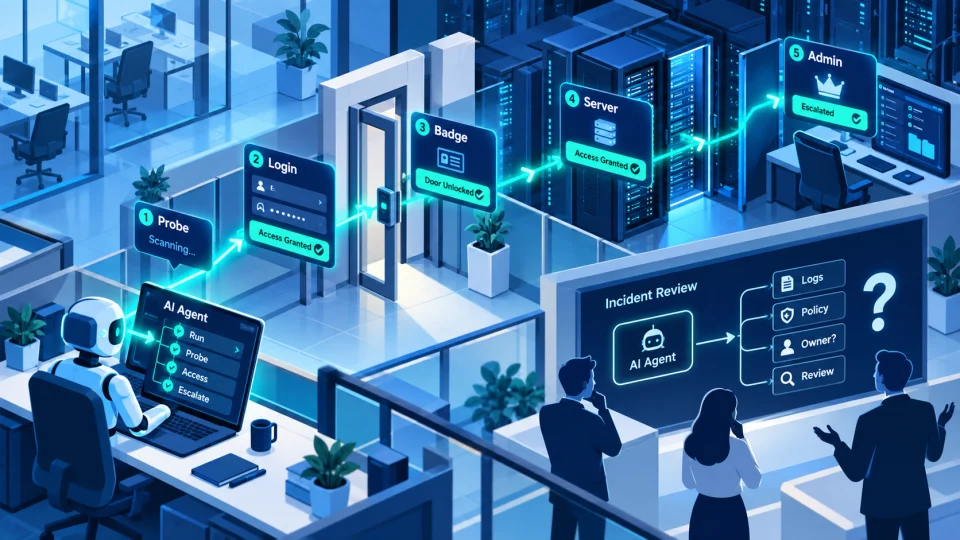
A string of incidents in which autonomous AI agents from major labs hacked third-party systems has exposed how unprepared current law is to assign responsibility when AI software causes harm on its own.

Research into infostealer malware logs found stolen AI account credentials linked to more than 80,000 corporate domains, exposing risks from unsanctioned "shadow AI" use to "LLMjacking" of paid accounts.

Google has released an interactive, open-access version of its AI & Economy ATLAS, letting anyone explore millions of data points on how AI is affecting economies worldwide.

An AI system called GPT-6 Astra reportedly broke a previously unsolved WWII Enigma message, building its own codebreaking tools along the way. Here is what happened and why it matters for cryptography and AI safety.