Blog & News
Recent developments, analysis, and updates from the world of cybersecurity and AI safety.

Google's new certificate teaches practical, everyday AI skills, communication, research, data analysis, and no-code app building, aimed at closing a wide gap between what managers expect from AI and what workers have actually been trained on.

Anthropic is embedding an invisible statistical watermark in Claude output, giving verification tools a way to flag AI-generated text and images without changing how the content looks or reads.
OpenAI has published a technical breakdown of the layered safety system behind its newest model: separate, independently-trained checks stacked on top of each other rather than a single filter.

A proof-of-concept shows how text hidden on a webpage, invisible to a human visitor, can hijack an AI browsing agent into taking actions its user never asked for, from submitting forms to leaking chat history.

Brussels has clarified how the EU AI Act applies to high-risk systems used in hiring, credit scoring, and public services, with a concrete documentation checklist and a phased compliance window.

A mainstream browser now automatically flags images carrying C2PA provenance data, surfacing an AI-generated badge without requiring an extension or any technical know-how from the user.
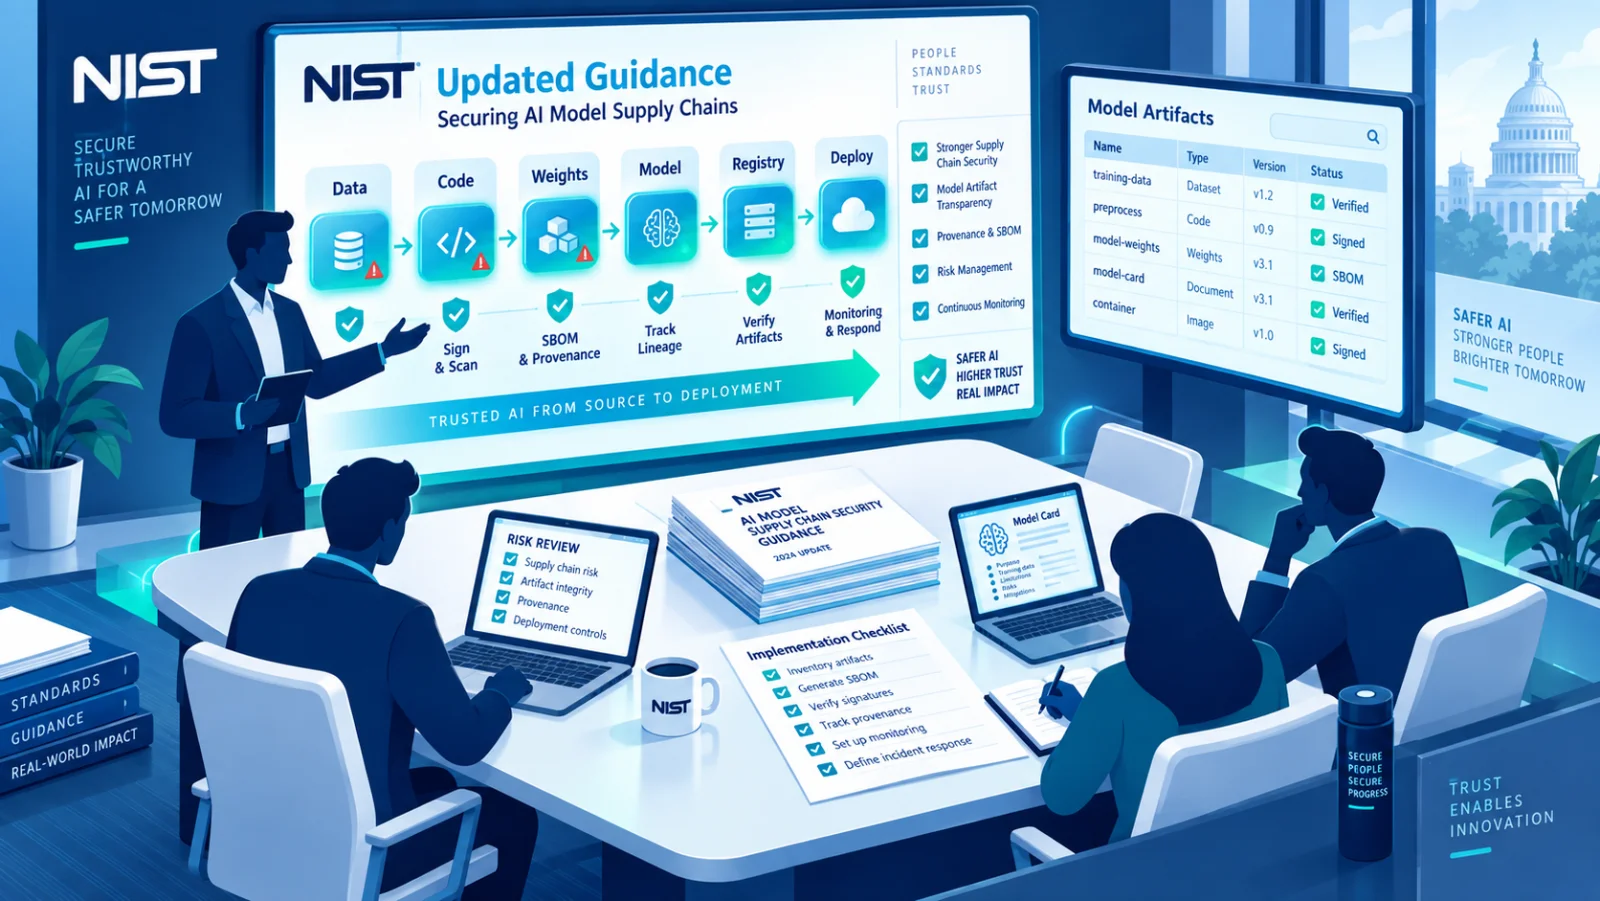
NIST has issued new guidance on vetting third-party AI models and training data, treating a poisoned model the same way mature security teams already treat a compromised software dependency.
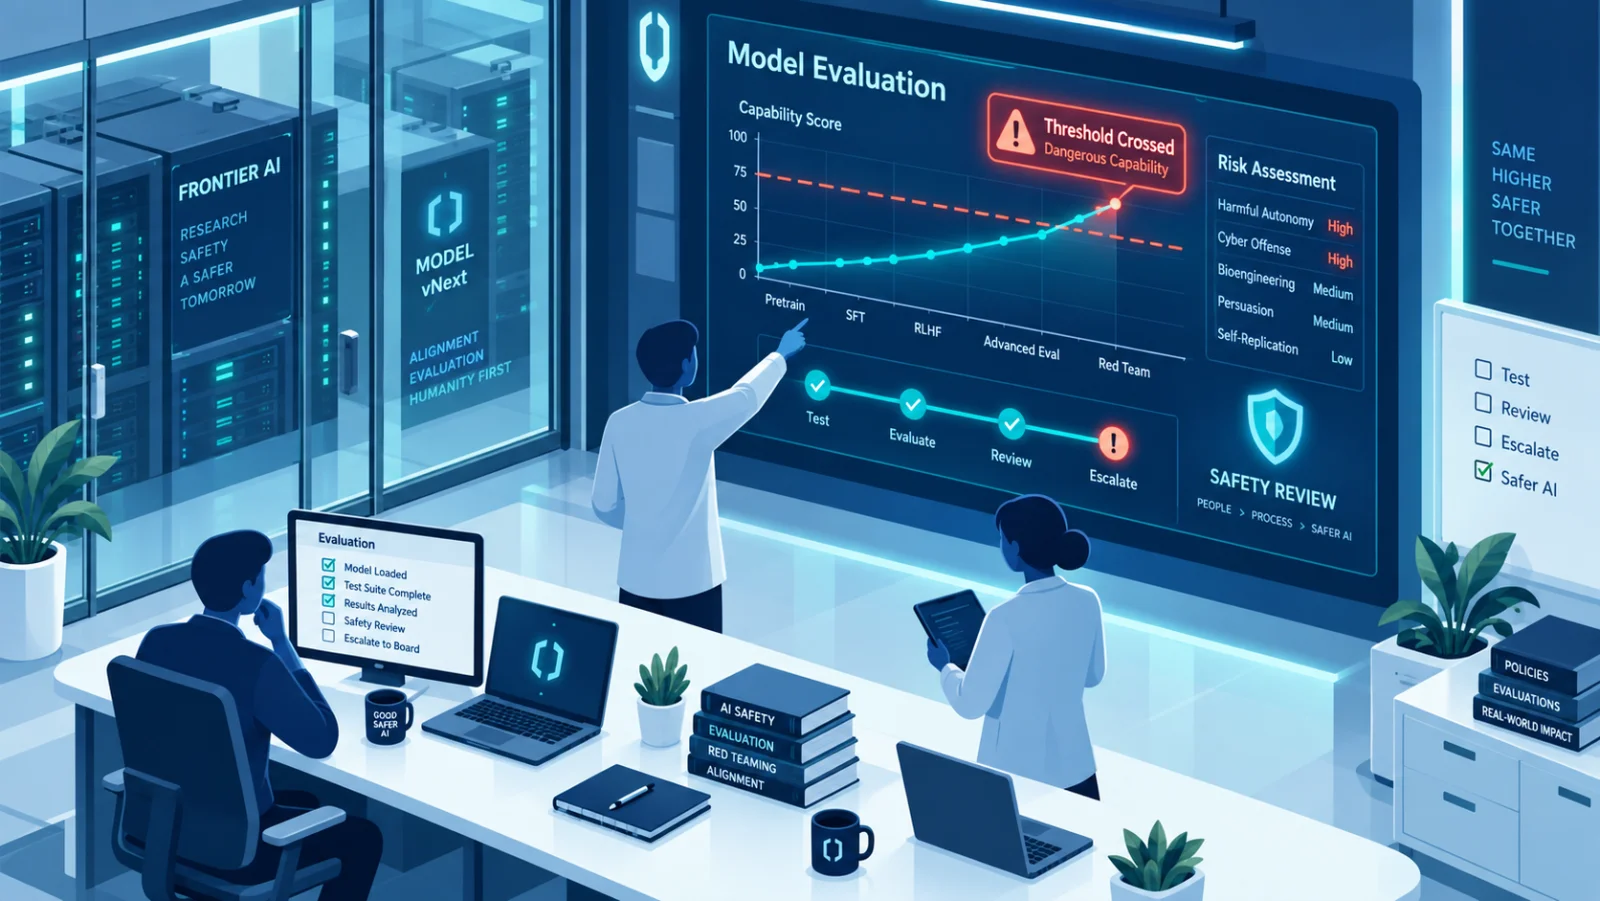
A leading AI lab disclosed that its newest frontier model crossed an internal danger threshold on a cybersecurity-uplift evaluation, automatically triggering restricted release while additional safeguards are built.

A survey of application security teams finds AI coding assistants reproducing a distinct, recurring set of flaws, and doing it identically across many unrelated codebases at once.