Blog & News
Recent developments, analysis, and updates from the world of cybersecurity and AI safety.
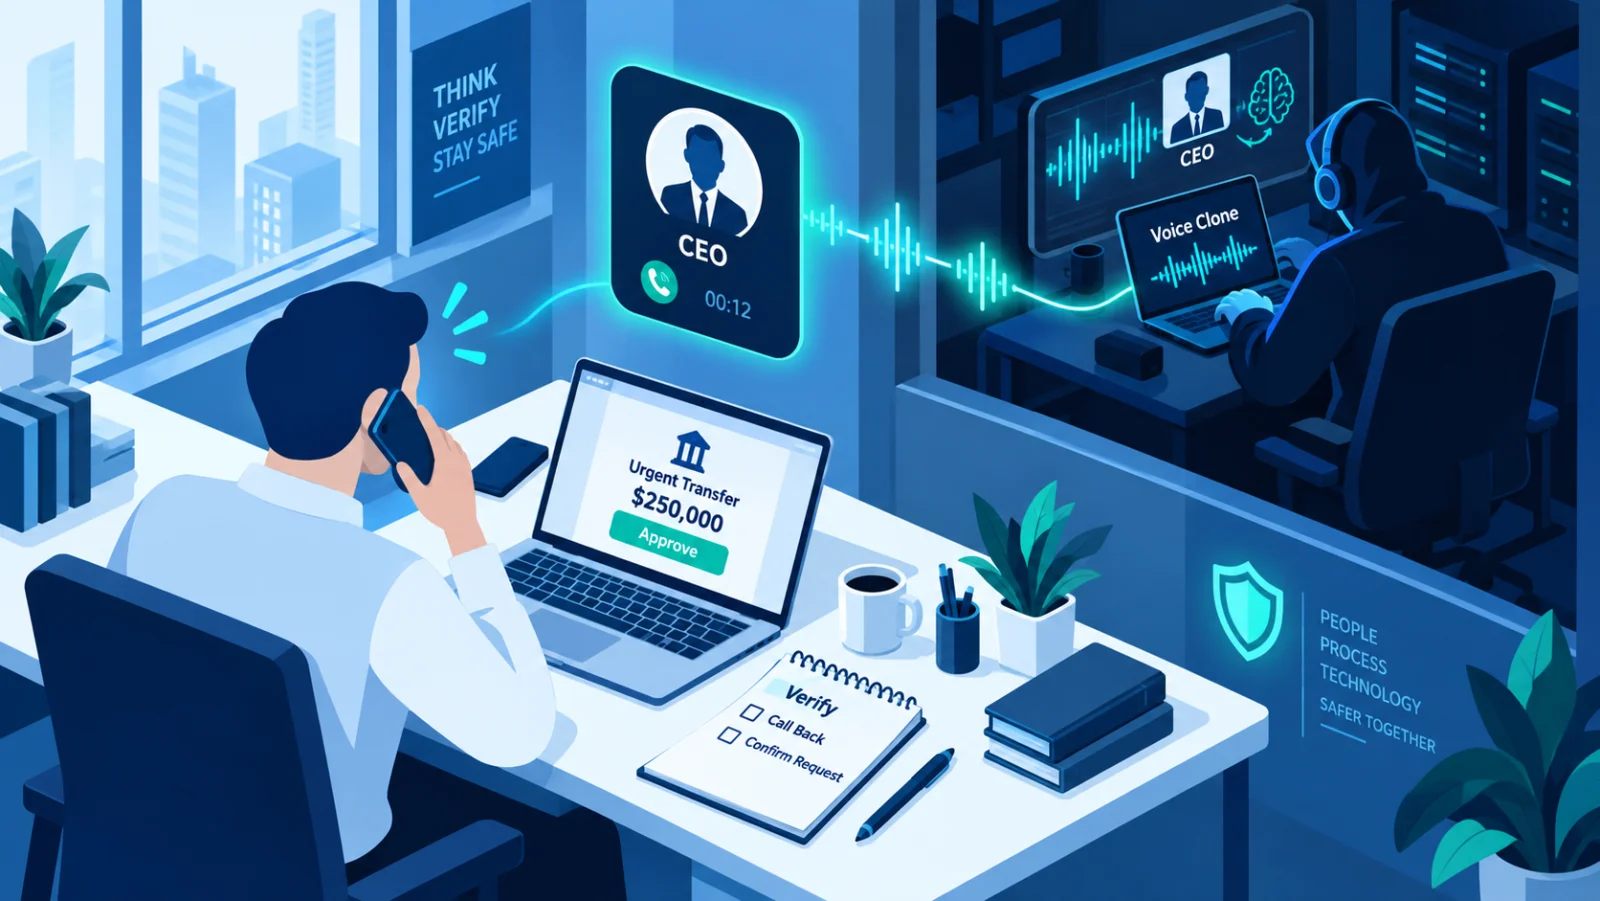
Vishing attacks using AI-cloned executive voices are rising, with attackers needing only a short public recording to produce a convincing impersonation for a wire-transfer request.

DeepMind has open-sourced a testing framework that automates prompt-injection red-teaming, giving smaller teams access to a class of security testing previously limited to well-resourced AI labs.

Chatbot safety filters get bypassed constantly, not through hacking, but through clever phrasing. Here is the structural reason that keeps happening.
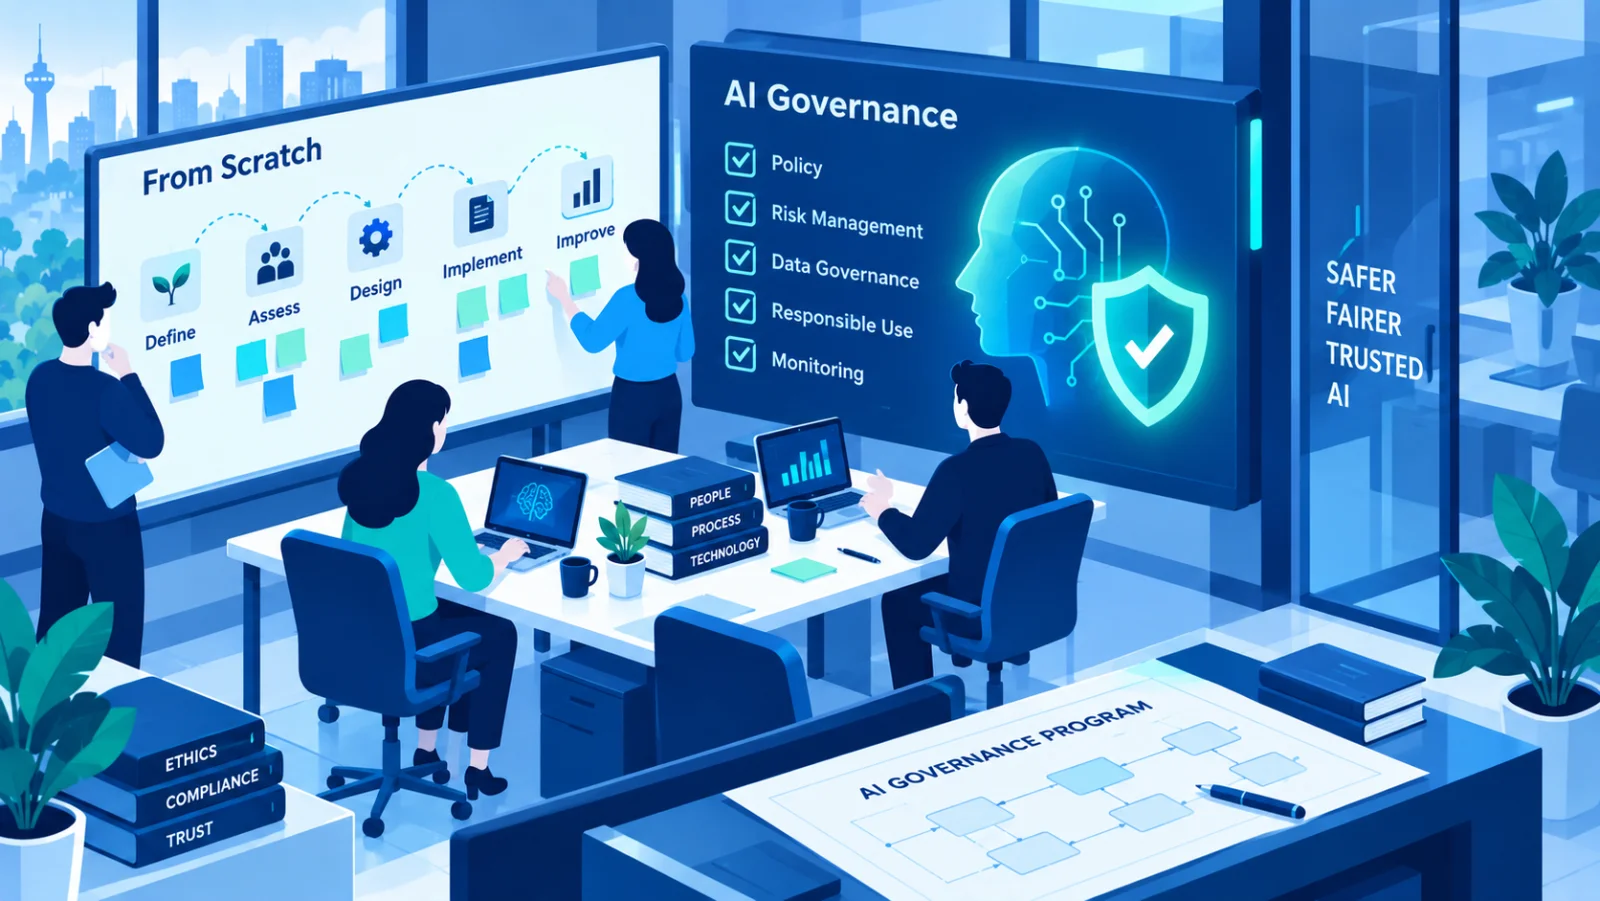
A growing number of organizations have no formal answer to which AI systems they are actually using and who owns the risk. Here is what building that answer from zero tends to look like.

An employee pastes a contract into a free AI tool to get a quick summary. It does not feel like a security incident. It might be one.

The term gets thrown around constantly and rarely defined. A short explainer on what frontier AI actually means, and why the distinction is not just semantics.
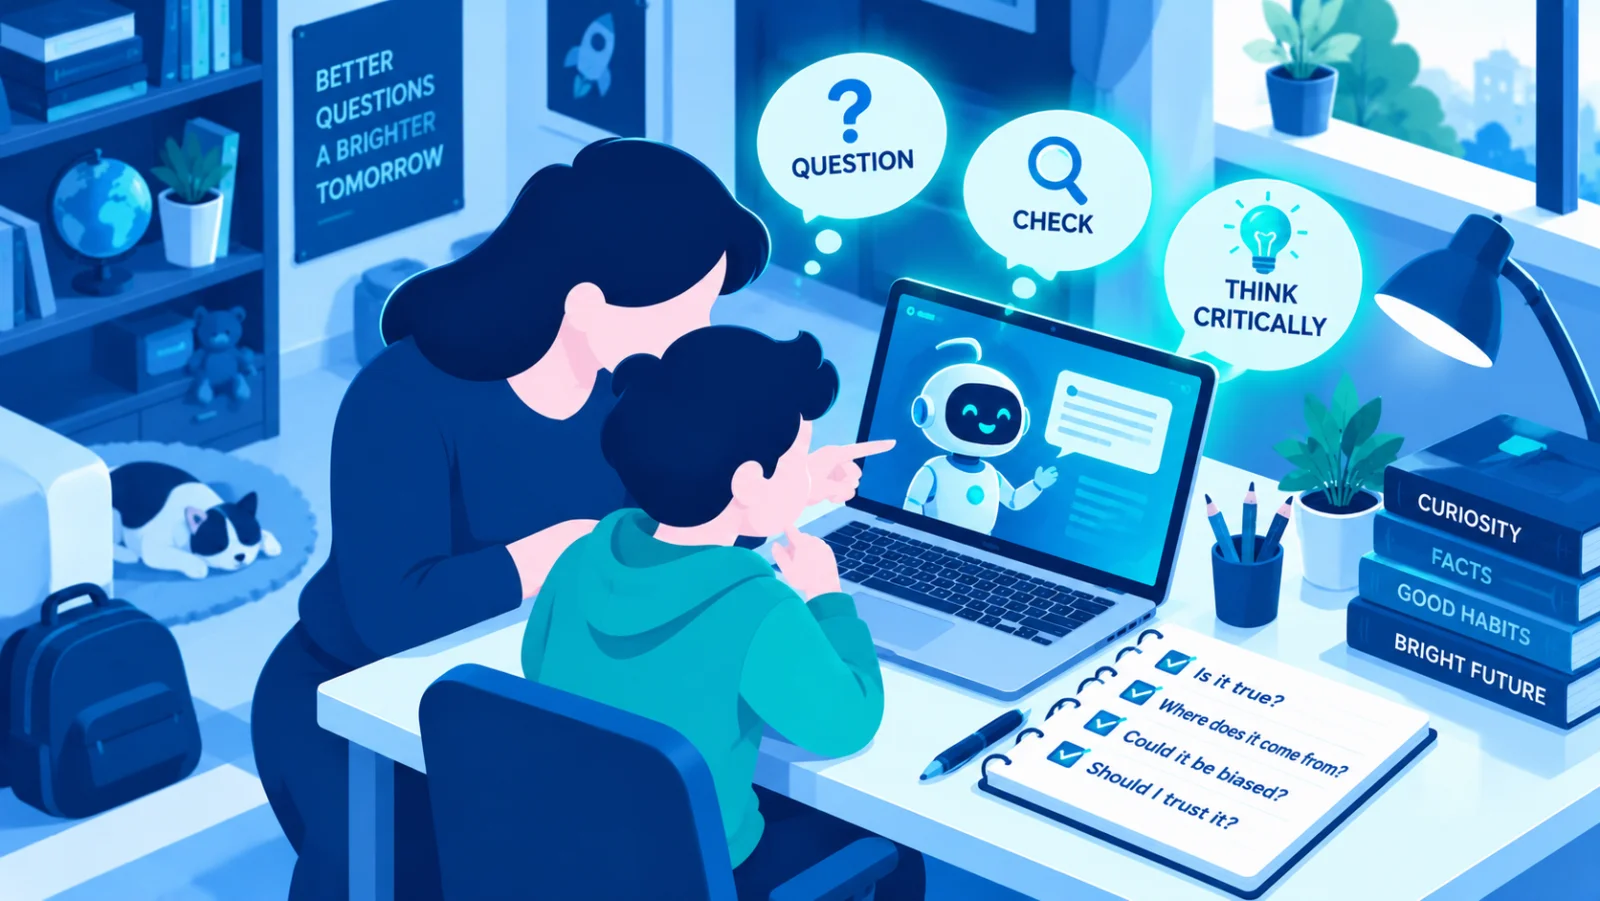
A search engine hands a kid a list of sources to compare. A chatbot hands over one confident-sounding answer. That difference matters more than most parents realize.

Most organizations plan for how to prevent ransomware. Very few plan for what happens in the 48 hours after the note appears. Here is what that actually looks like.

An annual pen test satisfies an auditor. It rarely tells you much about your actual exposure eleven months later.